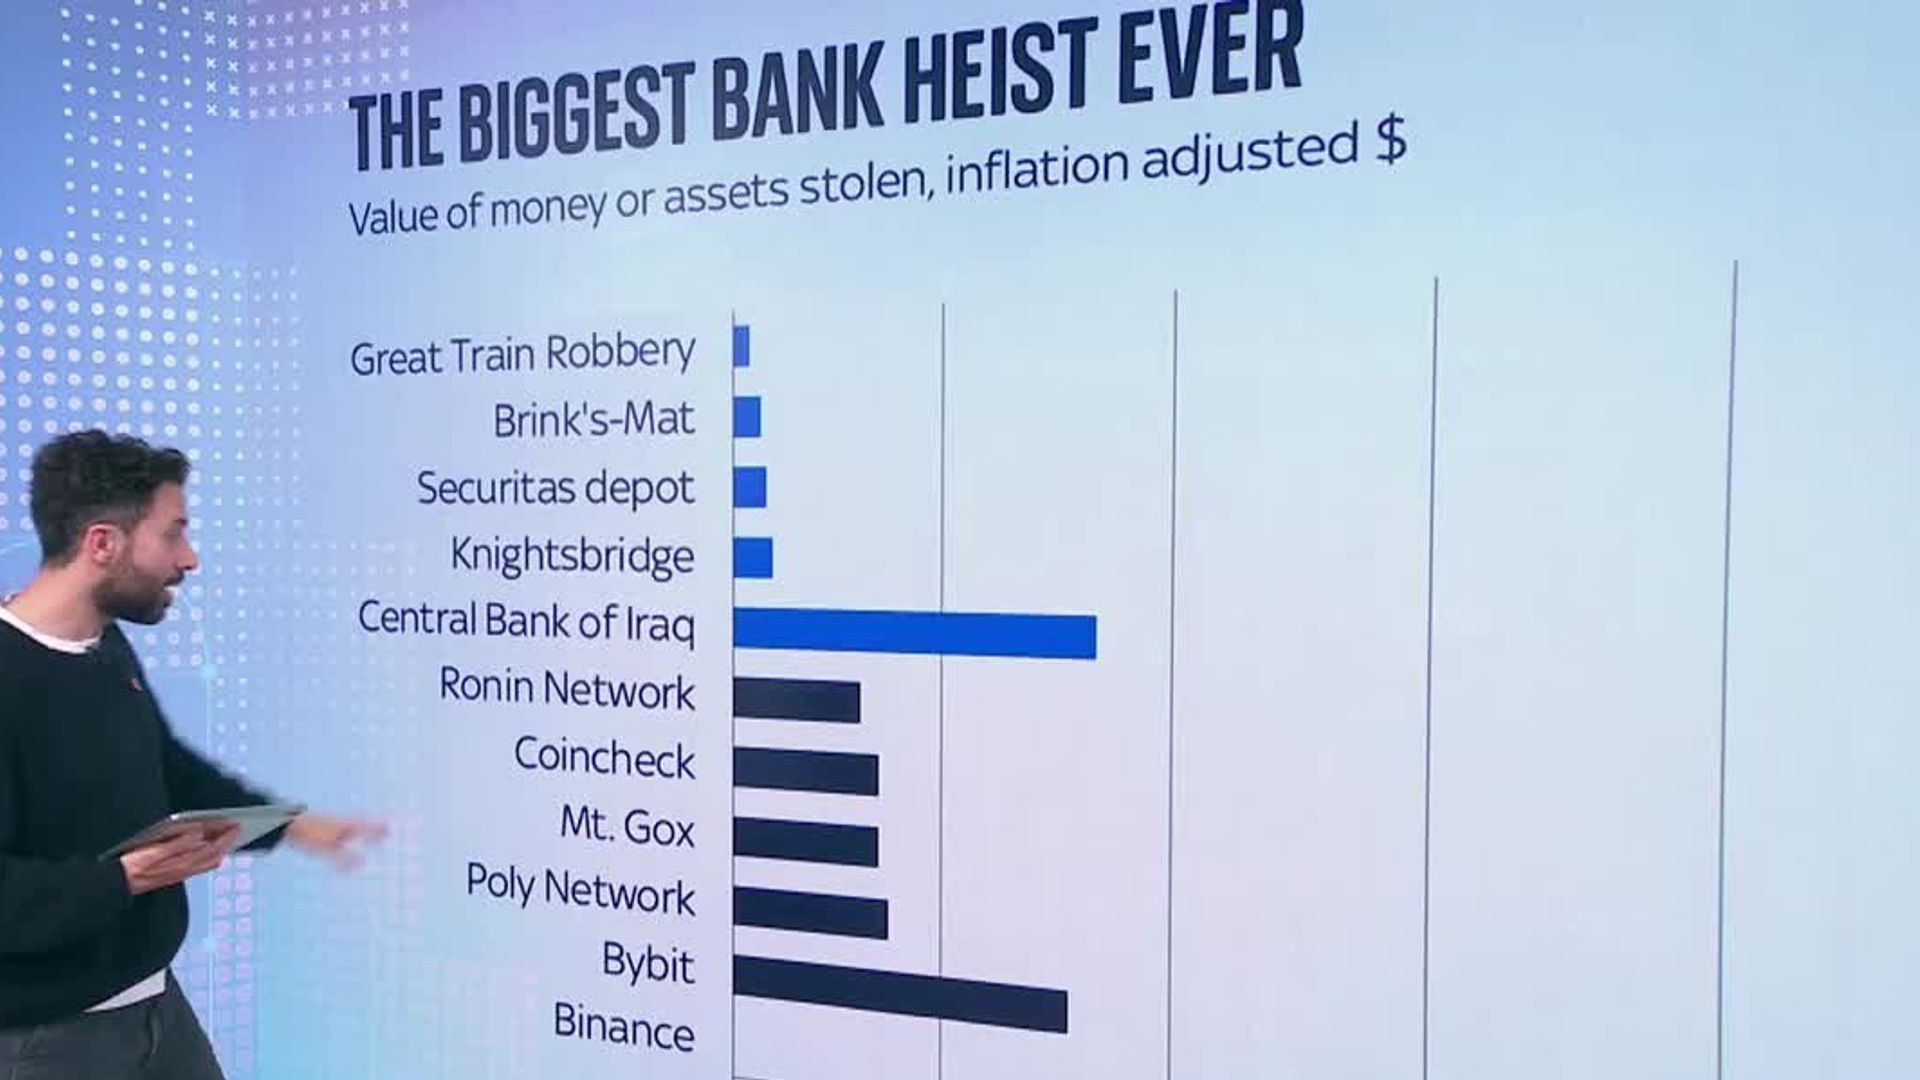
No high-tech robbers ever stole $6.3 billion from the Binance crypto exchange. The viral headline claiming a multi-billion-dollar digital heist against the world’s largest cryptocurrency platform is entirely fabricated, a phantom breach born from recycled clickbait, misunderstood blockchain transactions, and the industry's chronic vulnerability to rumor-driven panic.
In reality, the largest single theft in Binance’s actual operating history remains the October 2022 exploit of the BNB Smart Chain bridge, where attackers drained roughly $570 million in tokens—and even then, network validators froze the chain before the vast majority of those funds could leave the ecosystem. Yet every few months, variants of the "$6.3 billion Binance robbery" resurface across content farms, social media feeds, and low-tier aggregators.
Why does a fictional ten-figure heist gain traction so easily? Because in decentralized finance, the distance between a routine internal wallet transfer and a catastrophic bank run is often just one bad headline.
Anatomy of a Phantom Crypto Heist
To understand how a $6.3 billion myth takes hold, you have to look at how cryptocurrency exchanges move money behind the scenes. Unlike traditional banks, which settle ledgers privately behind closed doors, centralized crypto exchanges operate on public blockchains. Every time Binance consolidates user deposits from thousands of individual deposit addresses into a single cold storage vault, automated whale-tracking bots broadcast the movement to millions of traders in real time.
When an alert flashes across X or Telegram reading "100,000 BTC moved from Binance to unknown wallet," panic sells faster than facts can load. Bad actors, engagement farmers, and automated scraping sites seize on these massive, routine internal transfers. They slap an incendiary headline onto a real transaction hash, invent a narrative about "high-tech robbers," and watch the clicks roll in.
There is also a persistent confusion between exchange hacks, cross-chain bridge exploits, and regulatory penalties. Over the years, headlines involving Binance have regularly featured numbers in the billions:
- The $4.3 billion settlement with the U.S. Department of Justice and financial regulators in November 2023 over anti-money laundering failures.
- Daily trading volumes regularly exceeding tens of billions of dollars, creating massive on-chain liquidity shifts that look suspicious to untrained eyes.
- Proof-of-Reserve audits that require moving billions in collateral between wallets to verify solvency on-chain.
When algorithmic content generators mash these distinct news cycles together, a $4.3 billion legal fine or a $6 billion cold-wallet migration mutates into a fictional $6.3 billion robbery. Once published on a single domain, syndicate networks scrape and rewrite the story dozens of times, creating an illusion of independent verification where none exists.
What Actually Happened During Binance's Real Security Breaches
Dismissing a fake $6.3 billion theft does not mean Binance has an unblemished security record. Treating the exchange as invulnerable would be just as misleading as inventing imaginary losses. Over nearly a decade of operation, the platform and its adjacent infrastructure have suffered two major, verified security failures—both of which reveal far more about real-world crypto risk than any fabricated blockbuster heist.
The May 2019 Hot Wallet Breach
In May 2019, attackers compromised a large number of user API keys, two-factor authentication codes, and other validation data through a combination of phishing, viruses, and coordinated infiltration. The hackers executed a single, surgical transaction out of Binance’s hot wallet—the internet-connected pool of funds used to process rapid customer withdrawals—making off with 7,000 Bitcoin, worth approximately $40 million at the time.
Binance absorbed the loss entirely through its Secure Asset Fund for Users (SAFU), an emergency insurance pool funded by a percentage of trading fees. Customer balances remained intact, though withdrawals were frozen for a week while engineers overhauled internal security architecture.
The October 2022 BNB Chain Bridge Exploit
The closest Binance ever came to a multi-billion-dollar disaster occurred in October 2022, though it targeted the BSC Token Hub—a cross-chain bridge connecting the older BNB Beacon Chain to the BNB Smart Chain—rather than the centralized exchange's main custody vaults.
Attackers exploited a subtle cryptographic flaw in how the bridge verified proofs, allowing them to forge messages and mint 2 million BNB tokens out of thin air. At market prices, the newly minted tokens were valued at roughly $570 million.
The exploit exposed a fundamental tension in crypto infrastructure. While decentralized purists argue that blockchains should remain immutable regardless of theft, Binance coordinated rapidly with the network's concentrated set of validators to halt the entire BNB Smart Chain within hours. The emergency freeze trapped roughly $430 million of the stolen assets on-chain before the attacker could bridge them out to untraceable networks, limiting the net loss to around $100 million to $130 million.
Why Crypto Bridges Remain the Industry's Softest Target
If high-tech robbers were actually going to steal $6.3 billion in cryptocurrency today, they would almost certainly bypass an exchange's cold storage vaults and target a cross-chain bridge or a multi-signature smart contract.
Centralized exchanges store the overwhelming majority of customer funds in cold storage—offline hardware modules disconnected from the internet, requiring multiple physical keys held by geographically separated executives to authorize a single movement. Stealing billions from cold storage requires physical espionage, insider collusion, or catastrophic operational failure.
Cross-chain bridges, by contrast, are giant honeypots sitting directly on the public internet. Because Bitcoin cannot natively run on Ethereum, and Ethereum cannot natively run on Solana, bridges act as digital escrow agents. Users lock assets on one chain, and the bridge mints equivalent wrapped tokens on another.
Consider a hypothetical example of how a bridge vulnerability works. Imagine a digital vault holding $2 billion in locked collateral that relies on a software script to check whether a user actually deposited funds before releasing a receipt. If an attacker discovers a flaw in how that script reads digital signatures, they do not need to crack passwords or phish employees. They simply submit a malformed receipt that tricks the smart contract into believing a massive deposit occurred, draining the vault in a single block confirmation.
This exact mechanism powered the largest real crypto thefts in history, including the $625 million Ronin Network breach in 2022 and the $325 million Wormhole exploit the same year. Even combined, however, those historic attacks fall far short of the mythical $6.3 billion figure.
The Hidden Mechanics of Crypto Misinformation
Fake breach articles do not survive on accident. They thrive because specific incentives reward their creation across both traditional publishing and financial markets.
First, there is ad-arbitrage farming. High-drama keywords like "Binance," "robbers," and "billion" trigger massive click-through rates from retail investors terrified that their life savings have vanished. Low-quality websites publish sensationalized fiction, monetize the initial surge of panic traffic through programmatic display ads, and abandon the page before fact-checkers ever weigh in.
Second, there is market manipulation. In thin or anxious trading environments, spreading false rumors of exchange insolvency or massive theft can trigger cascading liquidations on leveraged derivatives platforms. Traders holding short positions profit directly when retail users panic-sell tokens on spot markets. Even a 3% dip across major assets translates into hundreds of millions of dollars in liquidated positions within minutes.
Third, SEO scraping loops compound the damage. When one site publishes a fabricated breach story, automated content aggregators ingest the text, spin the phrasing using basic language models, and republish it across dozens of mirror domains. Search engines and social algorithms temporarily mistake that sudden burst of duplicate URLs for breaking consensus news.
How to Verify a Crypto Breach in Under Two Minutes
When a headline claims an exchange has lost billions, relying on secondary blogs or social media screenshots guarantees you will get burned. Veteran analysts and on-chain investigators verify breach claims using direct, observable evidence before making any financial move.
- Check the official status channels and executive feeds directly. Major exchanges communicate infrastructure halts immediately via verified status pages and primary leadership accounts because silence accelerates bank runs. If a $6.3 billion theft actually occurred, withdrawals across the platform would freeze globally within minutes.
- Inspect the on-chain proof via block explorers. Real thefts leave permanent cryptographic footprints. Security firms like PeckShield, CertiK, and ZachXBT routinely publish the exact transaction hashes and attacker wallet addresses within minutes of an exploit. If an article fails to link a single Etherscan, BscScan, or Mempool transaction ID, the story lacks primary evidence.
- Distinguish between internal wallet sweeps and external outflows. When a large balance moves off an exchange hot wallet, trace where the destination address sends the funds. Legitimate cold-wallet sweeps go to dormant, multi-signature addresses with long histories of interacting exclusively with that exchange. Attackers immediately fragment funds across decentralized exchanges, cross-chain bridges, and privacy mixers.
- Watch the stablecoin and token peg behavior. Markets price in real disasters faster than journalists can type. During an actual multi-billion-dollar exchange insolvency—such as the collapse of FTX in November 2022—the exchange's native token crashes violently, and stablecoin withdrawal spreads widen immediately as institutional market makers pull liquidity. If BNB, Bitcoin, and USDT are trading normally with tight spreads, no $6.3 billion hole exists on the balance sheet.
The cryptocurrency sector has plenty of genuine risks—from smart contract bugs and phishing kits to regulatory crackdowns and custodianship failures—without inventing fictional $6.3 billion bank robberies. The next time a breathless headline claims high-tech thieves emptied an exchange's vaults overnight, look past the sensationalism and demand the transaction hash.